
The right way to Renew an Expired AD FS Certiticate
Learn this information to learn to renew expired certificates in Lively Listing Federation Service (AD FS) and their WAP servers.
Step 0: Overview the Drawback Background and Overview
Earlier immediately (eighth April 2025), my supervisor instructed me that the certificates in our AD FS servers had expired. He had already bought a brand new publicly signed certificates.
So, my job was to resume the certificates within the AD FS servers.
When an AD FS certificates expires, the service stops, and customers can’t entry it. Evidently, resolving this downside was a excessive precedence.
I’ve by no means carried out this job earlier than, so I did a couple of internet searches and located this text: ADFS: Altering the Certificates. The referenced article is nice, however it lined simply the steps to resume the AD FS certificates, not the WAP server certificates.
An additional search led me to a different article, – Substitute ADFS/WAP SSL certificates – which confirmed me the right way to renew the WAP servers’ certificates.
Whereas these referenced articles are nice, none supplied a complete step-by-step information to performing this all-important SysAdmin job. After efficiently renewing the certificates in my servers, I made a decision to doc the complete steps for my readers.
Listed here are they’re:
Step 1: Get a New Publicly Signed Certificates
This step is clear, however I included it for completeness. You may order a certificates from any certificates supplier.
In the meantime, you will need to be certain that the certificates meets the necessities outlined in necessities for ADFS tlsssl certificates.
Step 2: Add a Temp Self-Signed Wildcard Cert to ADFS
Since ADFS requires some certificates to perform, use the steps under to create and add a short lived self-signed wildcard certificates to the first AD FS Server.
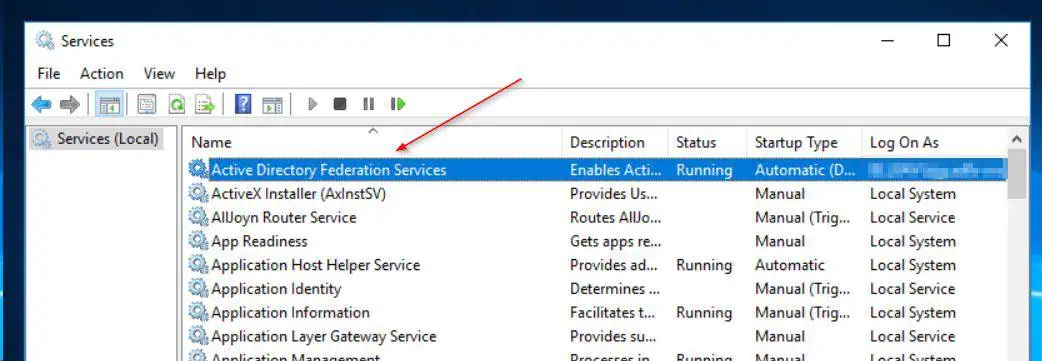
- If the AD FS service is stopped, begin it. To do that, seek for and open the Providers MMC, right-click the Lively Listing Federation Providers service, and choose Begin.
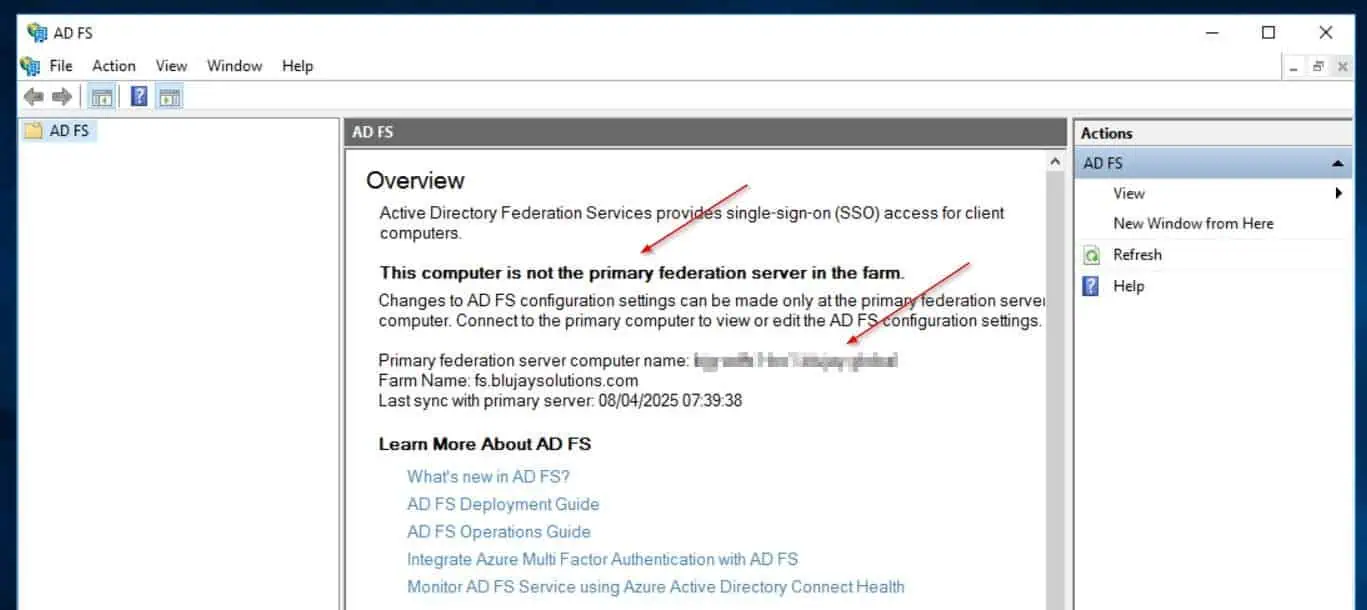
- To verify that the AD FS server you’re signed in to is the first server, open the AD FS Administration console through Server Supervisor.

If the server is the first server, it would show the AD FS providers. The secondary Federation server – see my second screenshot under – is not going to show the AD FS service.

The secondary server additionally shows the first federation server (blurred in my screenshot under).
- Check in to the first AD FS server and open Home windows PowerShell as administrator. Then, run the command under to get the standing of the prevailing certificates.
Get-ADFSCertificate –CertificateType token-signing
As seen within the certificates’s Not After property, it expired in March 14th 2025.

- After that, allow certificates rollover and generate a brand new certificates by working these instructions.
Set-ADFSProperties -AutoCertificateRollover $true
Replace-ADFSCertificate –CertificateType token-signing

- Lastly, confirm that the self-signed cert has been assigned to the AD FS server by working the Get-ADFSCertificate command once more:
Get-ADFSCertificate –CertificateType token-signing
The command’s outcomes ought to record two certificates. One ought to have a Not After date sooner or later, whereas the opposite ought to have the IsPrimary worth False.


Step 3: Import the New Public Signed Cert to the AD FS Server’s Native Retailer
Carry out the steps on this part on the major and secondary AD FS servers.
- Double-click the PFX file of the certificates you bought from a certificates supplier in Step 1. Then, on the primary web page of the import wizard, choose Native Machine.
Should you select the primary possibility—Present person—you received’t have the ability to set the AD FS server to make use of this certificates later on this information.
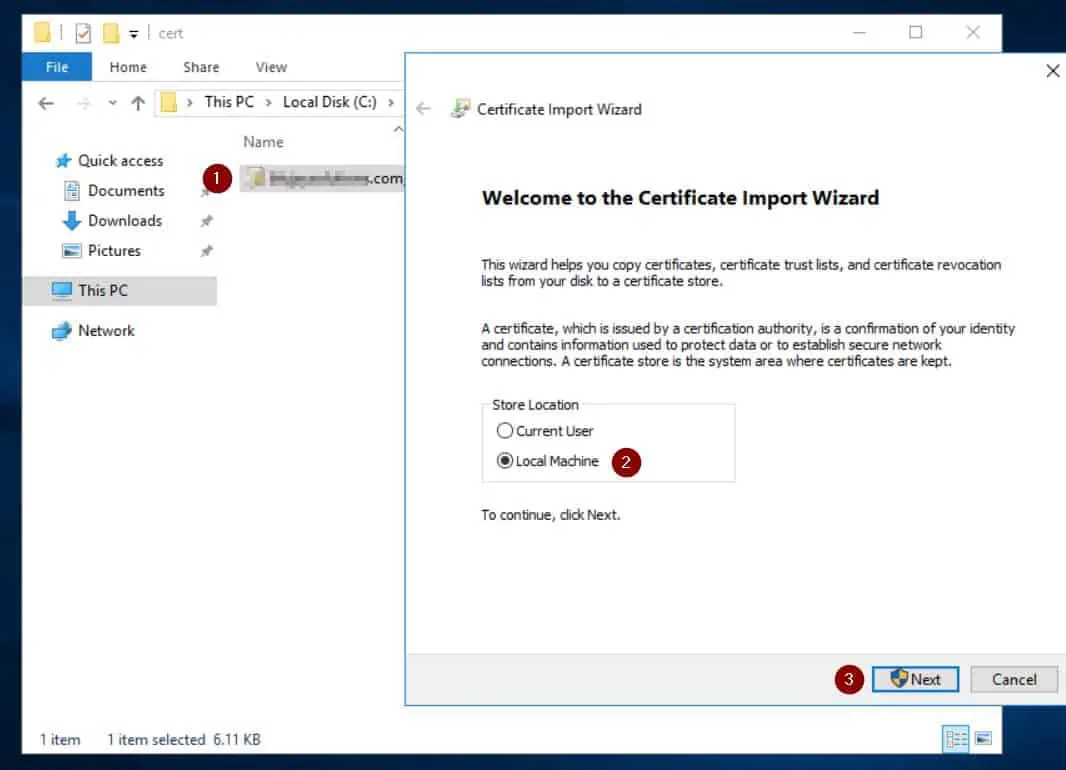
- The certificates’s file path can be displayed on the next web page. Click on Subsequent to proceed to the following web page.

- Lastly, enter the certificates’s PFX password and import it to the native pc’s certificates retailer. See my screenshots under for steering.
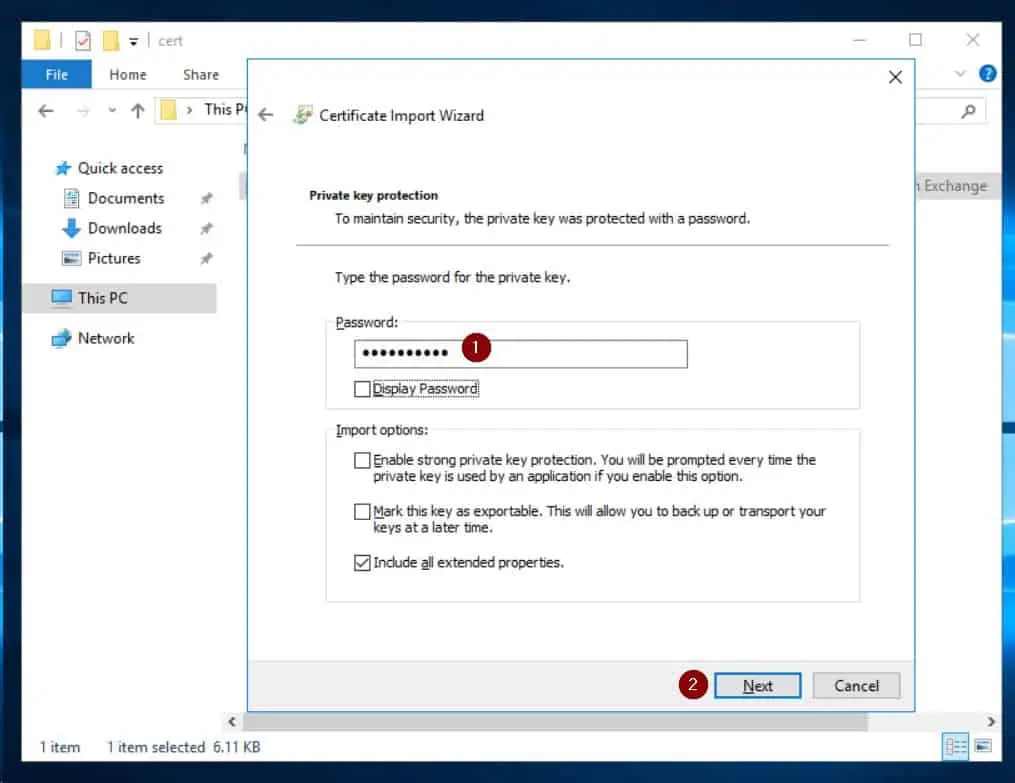
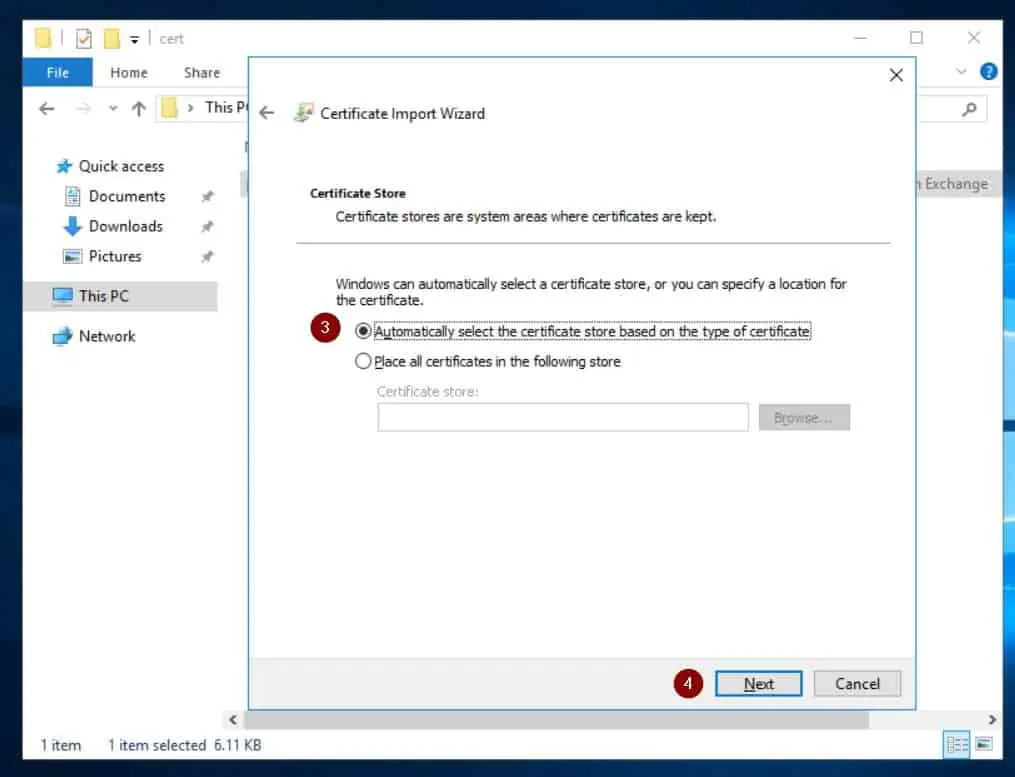
Repeat the above steps within the secondary AD FS server. Then, run the command under on the major server to disable the AD FS certificates rollover.
Set-ADFSProperties -AutoCertificateRollover $false
Step 4: Grant the AD FS AD Service Account Entry to the Cert Non-public Key
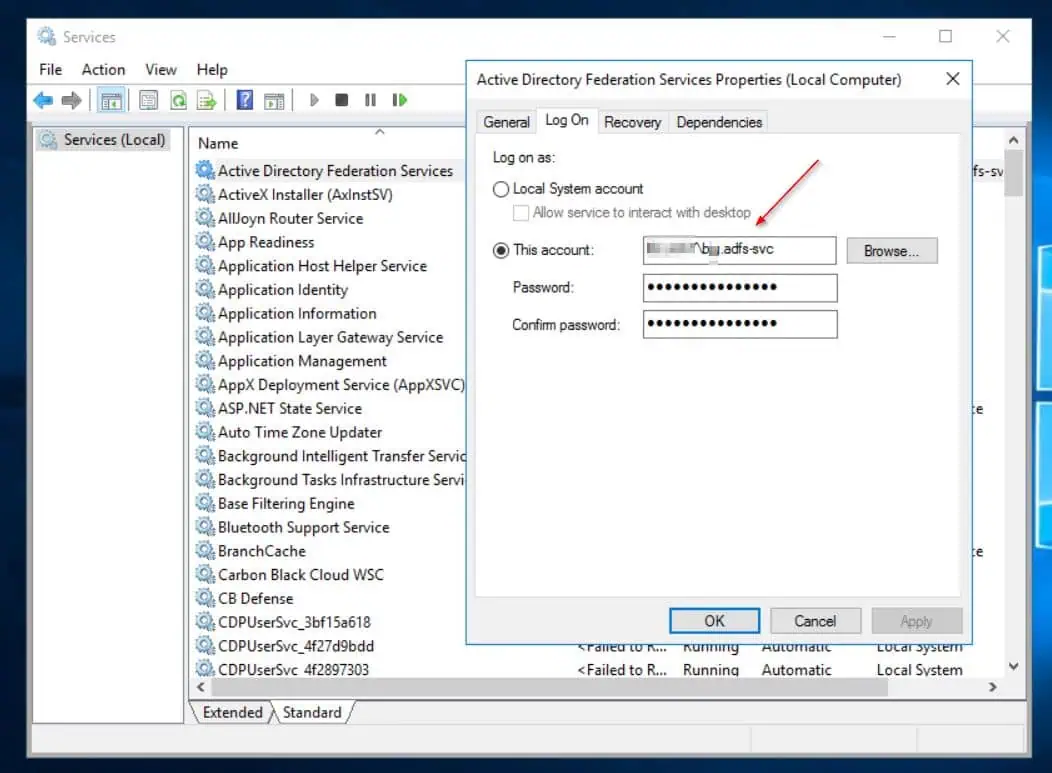
- Get the identify of the Lively Listing Service account for AD FS from the Log On tab of the properties of the Lively Listing Federation Providers service. You require this account later on this part.
Seek for and open Providers. Then, right-click Lively Listing Federation Providers, choose Properties, then the Log On tab.
- Seek for and open MMC as administrator (right-click MMC from the search consequence and select Run as administrator).

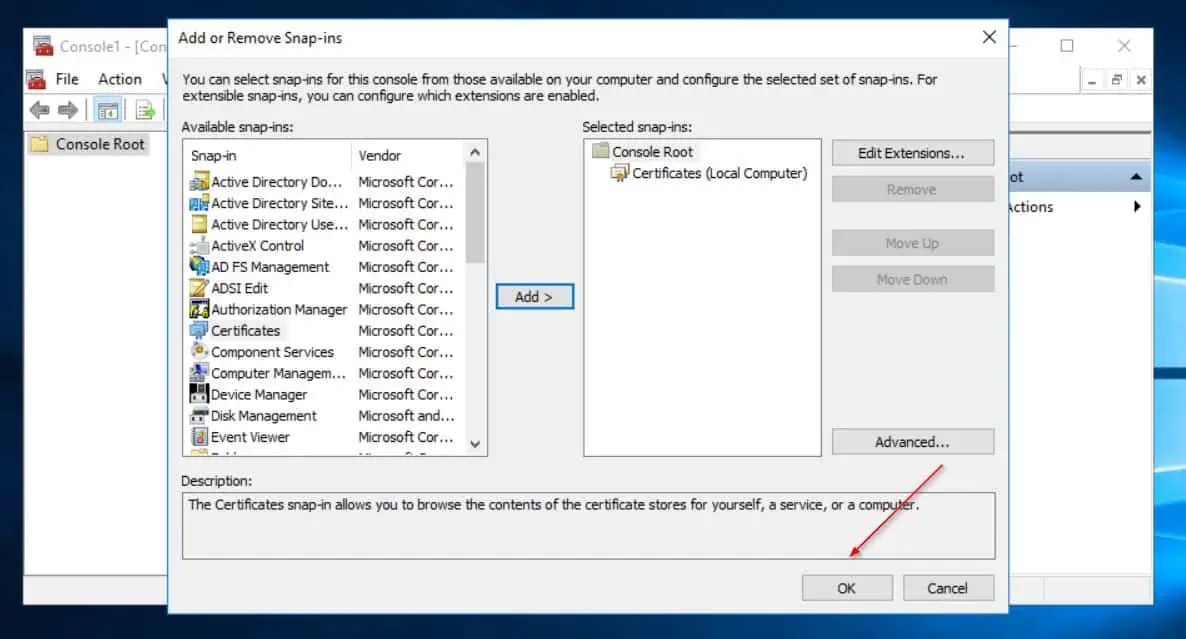
- Then, on the MMC, click on File and choose Add/Take away snap-in…Then, choose Certificates > Add.
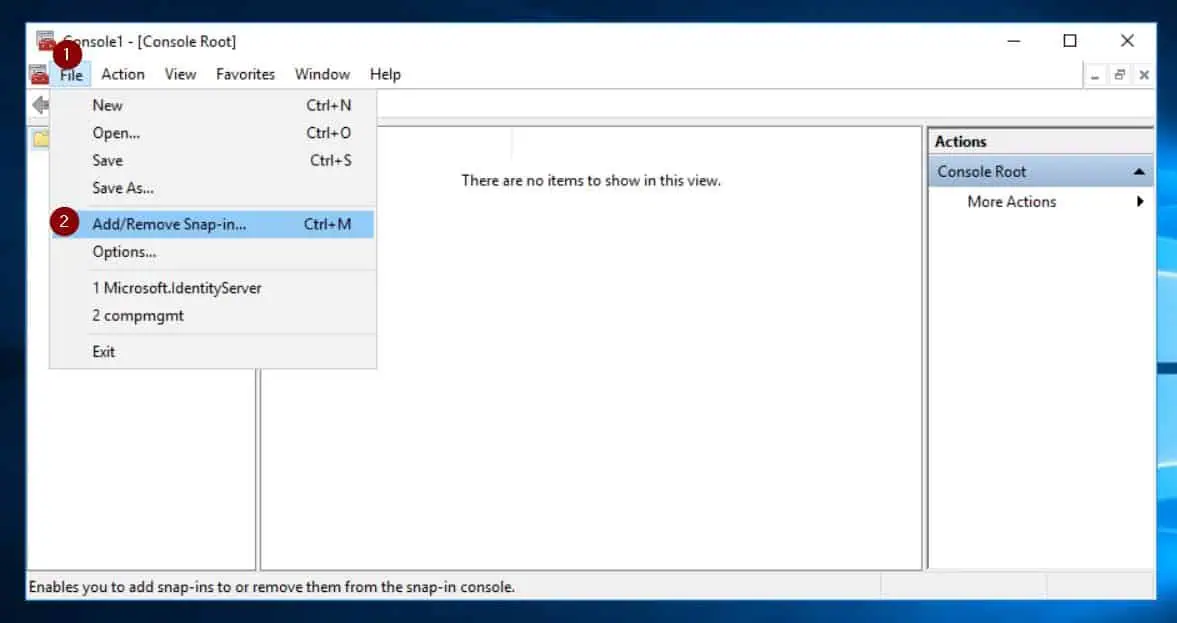

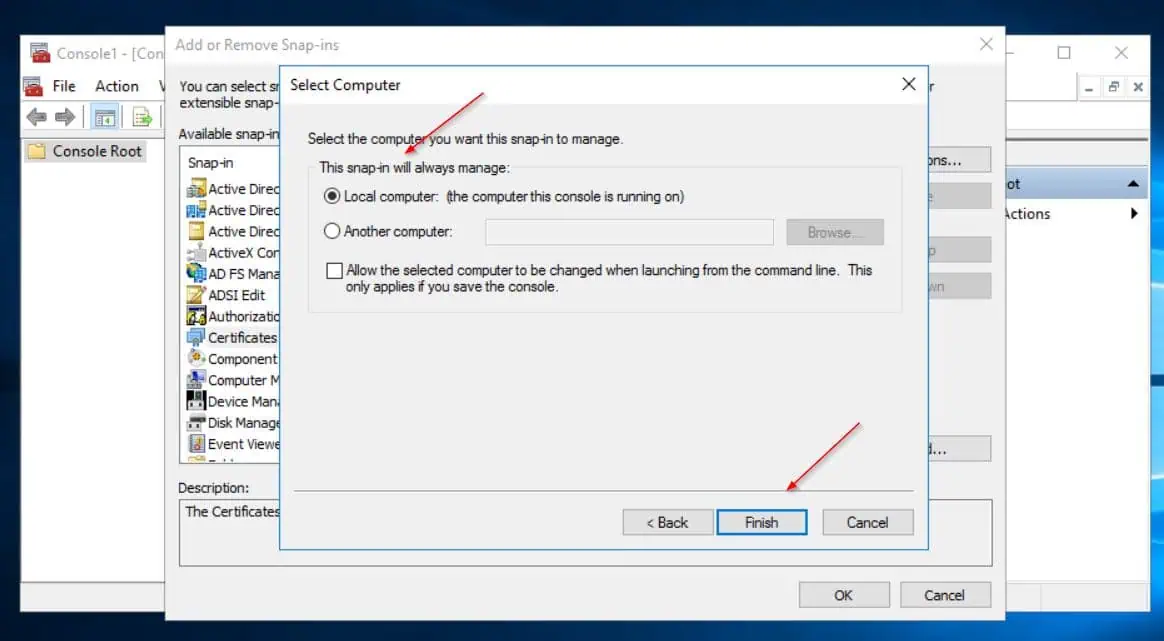
- Subsequent, select Pc account on the Certificates snap-in wizard, then click on Subsequent. Lastly, select Native pc (the pc this console is working on), then choose End, OK. See my screenshots under for steering.

- Broaden Certificates (Native pc), Private and left-click Certificates on the MMC console. Then, right-click the certificates you imported in Step 3 and level to All Duties > Handle Non-public Keys.
The latest cert ought to have an expiry date sooner or later.

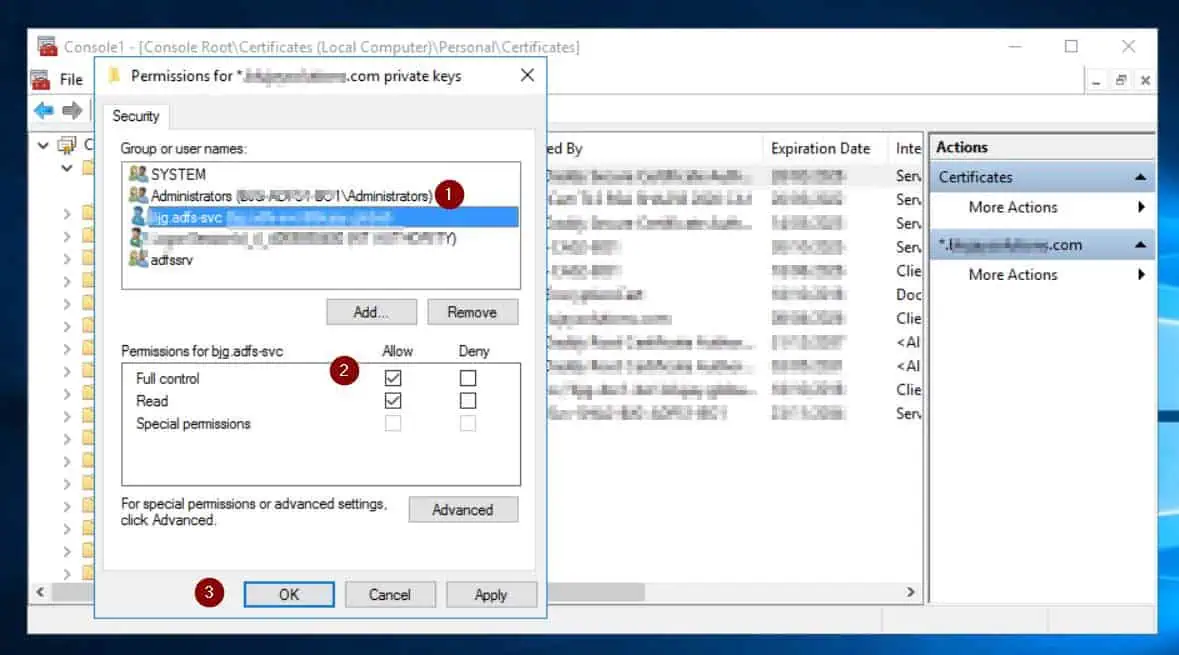
- The above motion opens the Permissions properties for the certificates’s personal keys. Click on the Add button.

- Then, click on Object Varieties > Choose Service Accounts, OK. After that, enter the identify of your AD FS service account within the Enter the item names to pick subject and grant it full management.

Repeat steps 1 to five above within the secondary AD FS server.
Step 5: Renew the Certificates within the AD FS Servers
- Launch the AD FS administration console (through Server Supervisor). Then, develop Service > Certificates and select Set Service Communication Certificates.
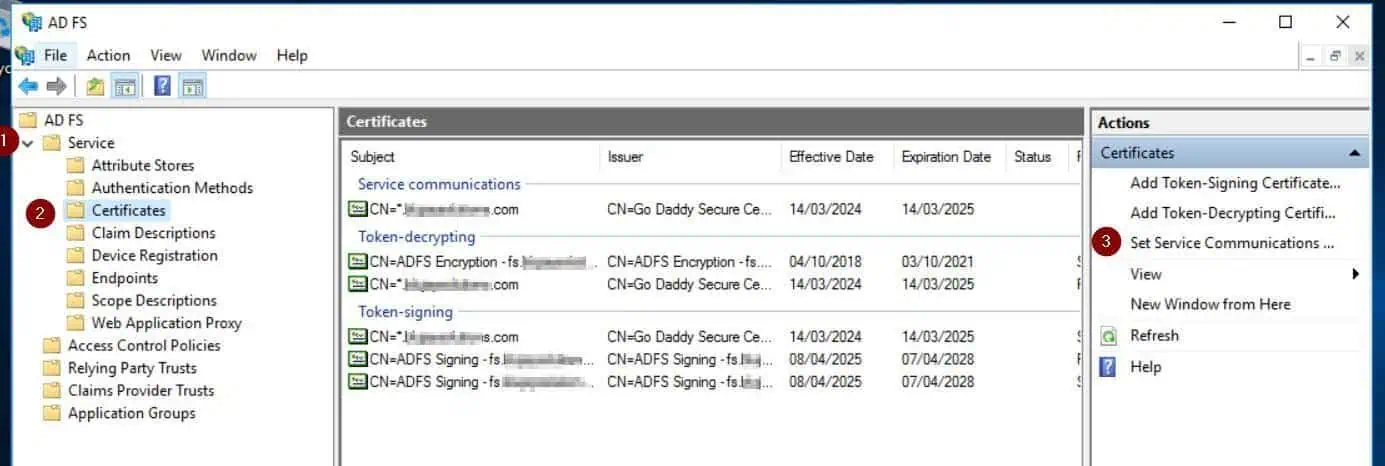
- On the Home windows Safety pop-up, choose Extra selections. Then, select the brand new certificates and click on OK.


- Repeat steps 1 and a pair of above to interchange the Token-decryption and Token-signing certs. Lastly, delete all of the previous certificates.
- Once you end the above steps, the brand new certificates ought to be listed for the Service communications, Token-decryption, and Token-signing sections of the Certificates blade.
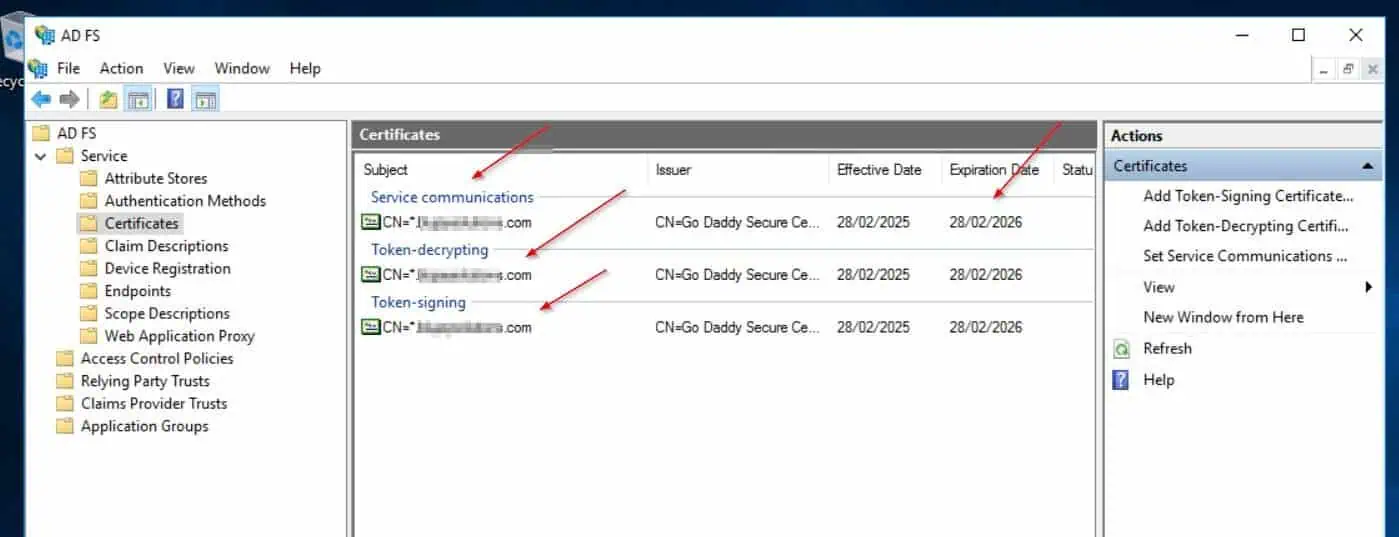
- After that, get the certificates’s thumbprint by right-clicking it, deciding on View Certificates, and selecting the Particulars tab > Thumbprint. Then, choose and duplicate the certificates’s thumbprint with Ctrl + C.


- Paste the thumbprint in a notepad and take away all areas.

- Run the command under – from the PowerShell console you opened as administrator – to re-enable AD FS rollover. Then, affirm that the brand new certificates is out there in AD FS by working the second command.
Set-ADFSProperties -AutoCertificateRollover $true
Get-adfsCertificate
- After that, set the AD FS server to make use of the brand new cert by working the command under. Substitute all the things in daring together with your cert Thumbprint.
Set-AdfsSslCertificate -Thumbprint <enter your certificates thumprint right here>
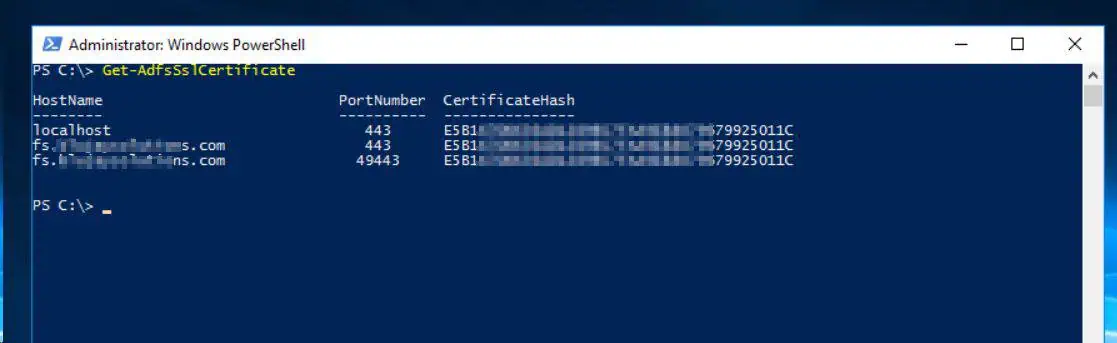
- Then, set the cert rollover to true and restart the ADFS service. Lastly, run the Get-AdfsSslCertificate command to verify that the AD FS server makes use of the brand new certificates.
Set-ADFSProperties -AutoCertificateRollover $true
Restart-Service ADFSSRV
Get-AdfsSslCertificate

Step 6: Renew the Certificates on the AD FS WAP Servers
- Copy the PFX file of the general public signed certificates to your first AD FS WAP server and repeat Step 3 (hyperlink opens in a brand new browser tab) part of this information.
- After that, open PowerShell as administrator and run these instructions.
#1. Configure the WAP service to make use of the brand new certificatesSet-WebApplicationProxySslCertificate -Thumbprint <enter your certificates thumprint right here>
#2. Re-establish the proxy belief of the WAP server with the AD FS server. This command will immediate you to enter an AD account with permissions to the AD FS service
Set up-WebApplicationProxy -CertificateThumbprint <enter your certificates thumprint right here> -FederationServiceName <enter your AD FS federation service FQDN right here>
#3. Lastly, replace the SSL cert for each printed app
Get-WebApplicationProxyApplication | Set-WebApplicationProxyApplication -ExternalCertificateThumbprint <enter your certificates thumprint right here>


- Repeat steps 1 and a pair of above in your second WAP server.
Conclusion
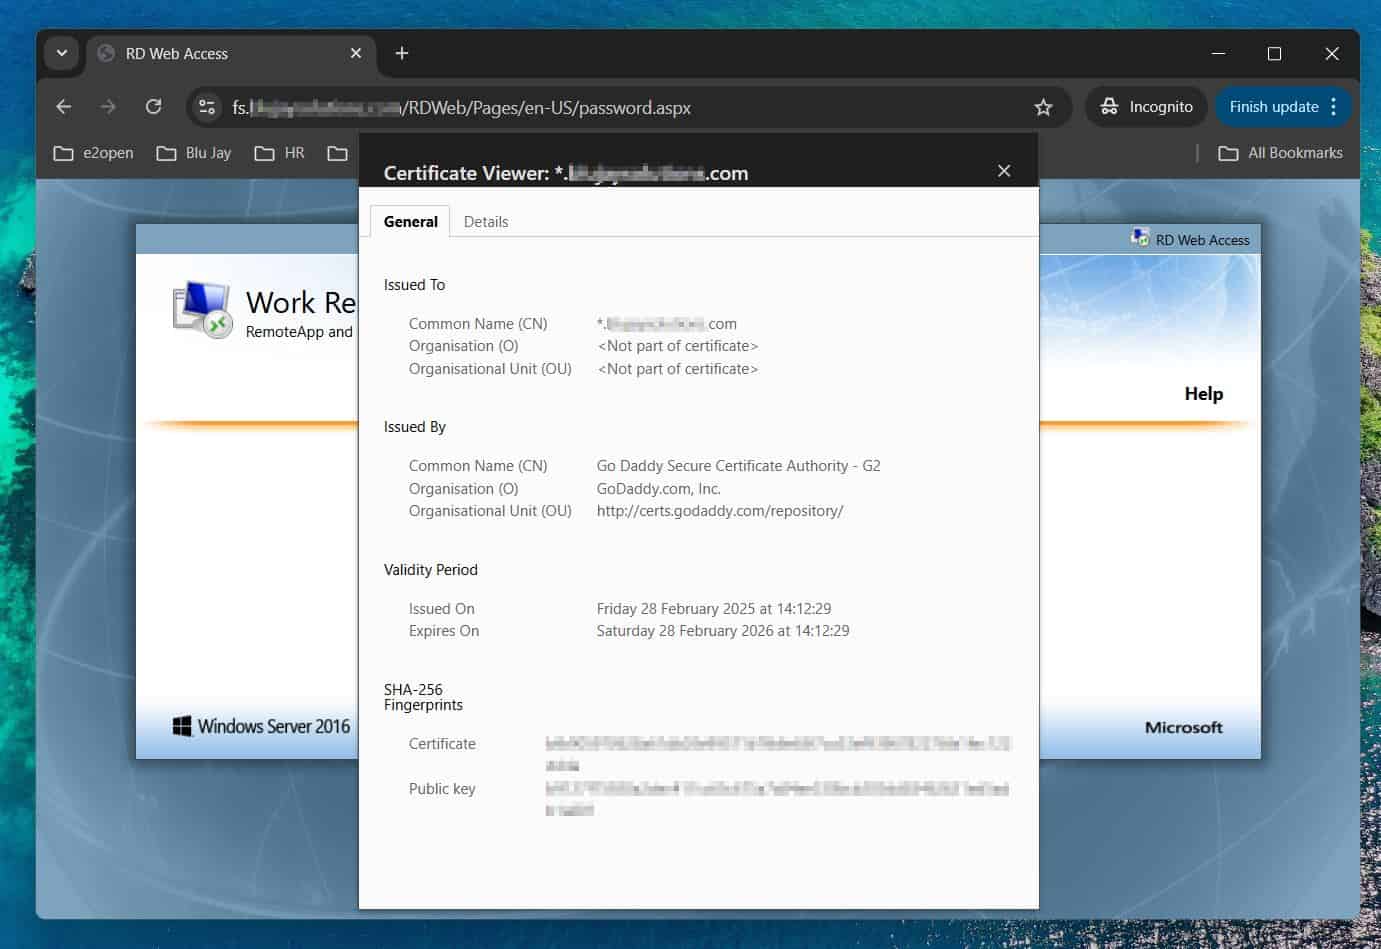
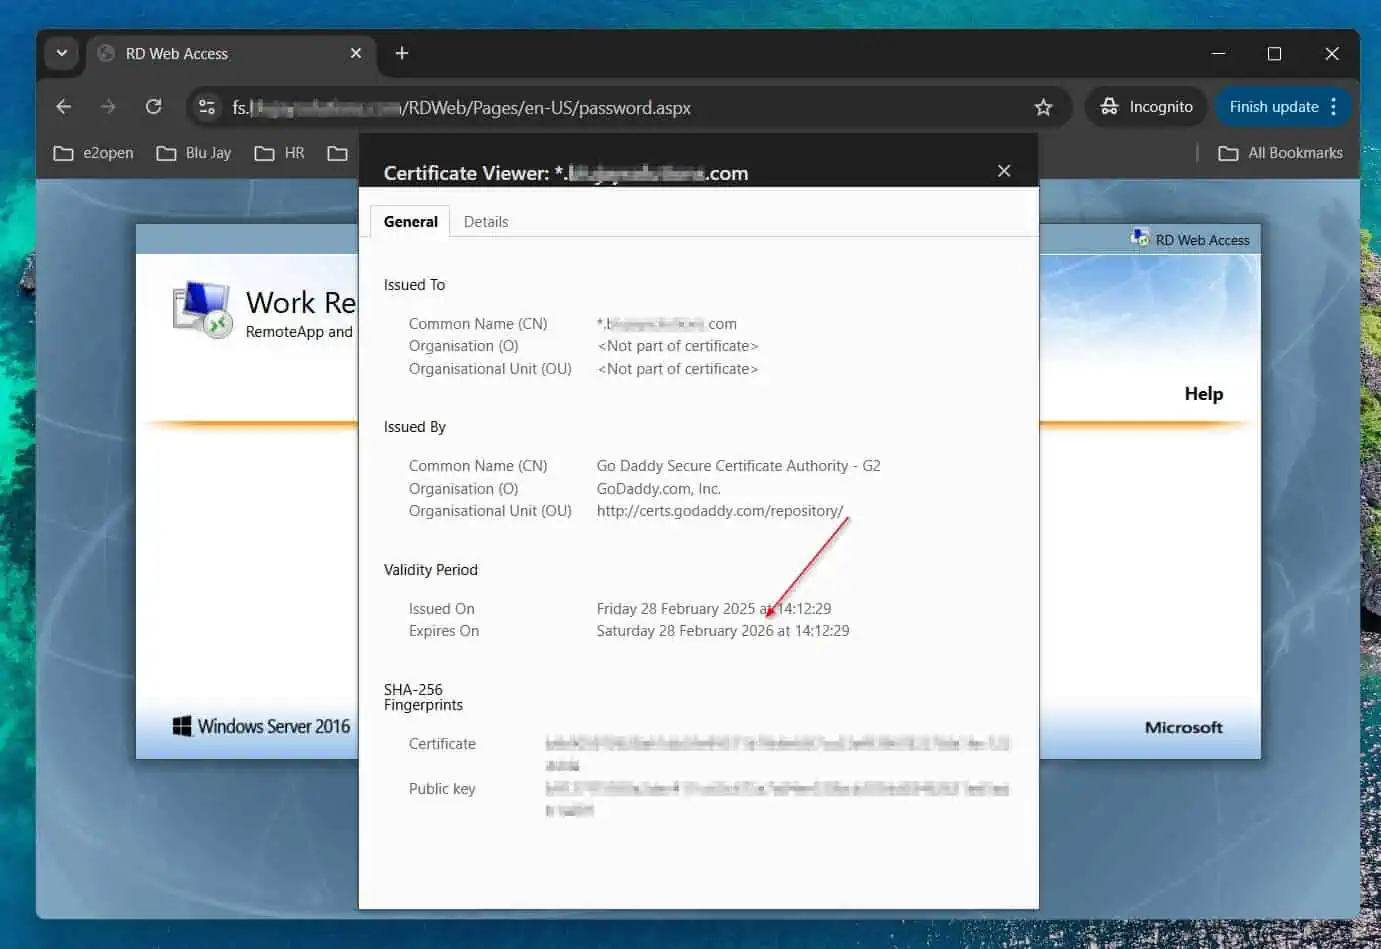
After finishing the steps outlined on this detailed information, once you open the front-end web site of your AD FS service on a browser, it would now not show a certificates error. Moreover, in the event you open the location’s certificates, it ought to show the brand new certificates.
I admit that renewing a certificates in an AD FS server is comparatively complicated. Following this detailed information, I’m assured you could have accomplished the duty efficiently, however I might nonetheless like to listen to your ideas.
Let me know what you concentrate on this information and in the event you met your objective by following it. You may present suggestions by responding to our “Was this web page useful?” suggestions request under.